


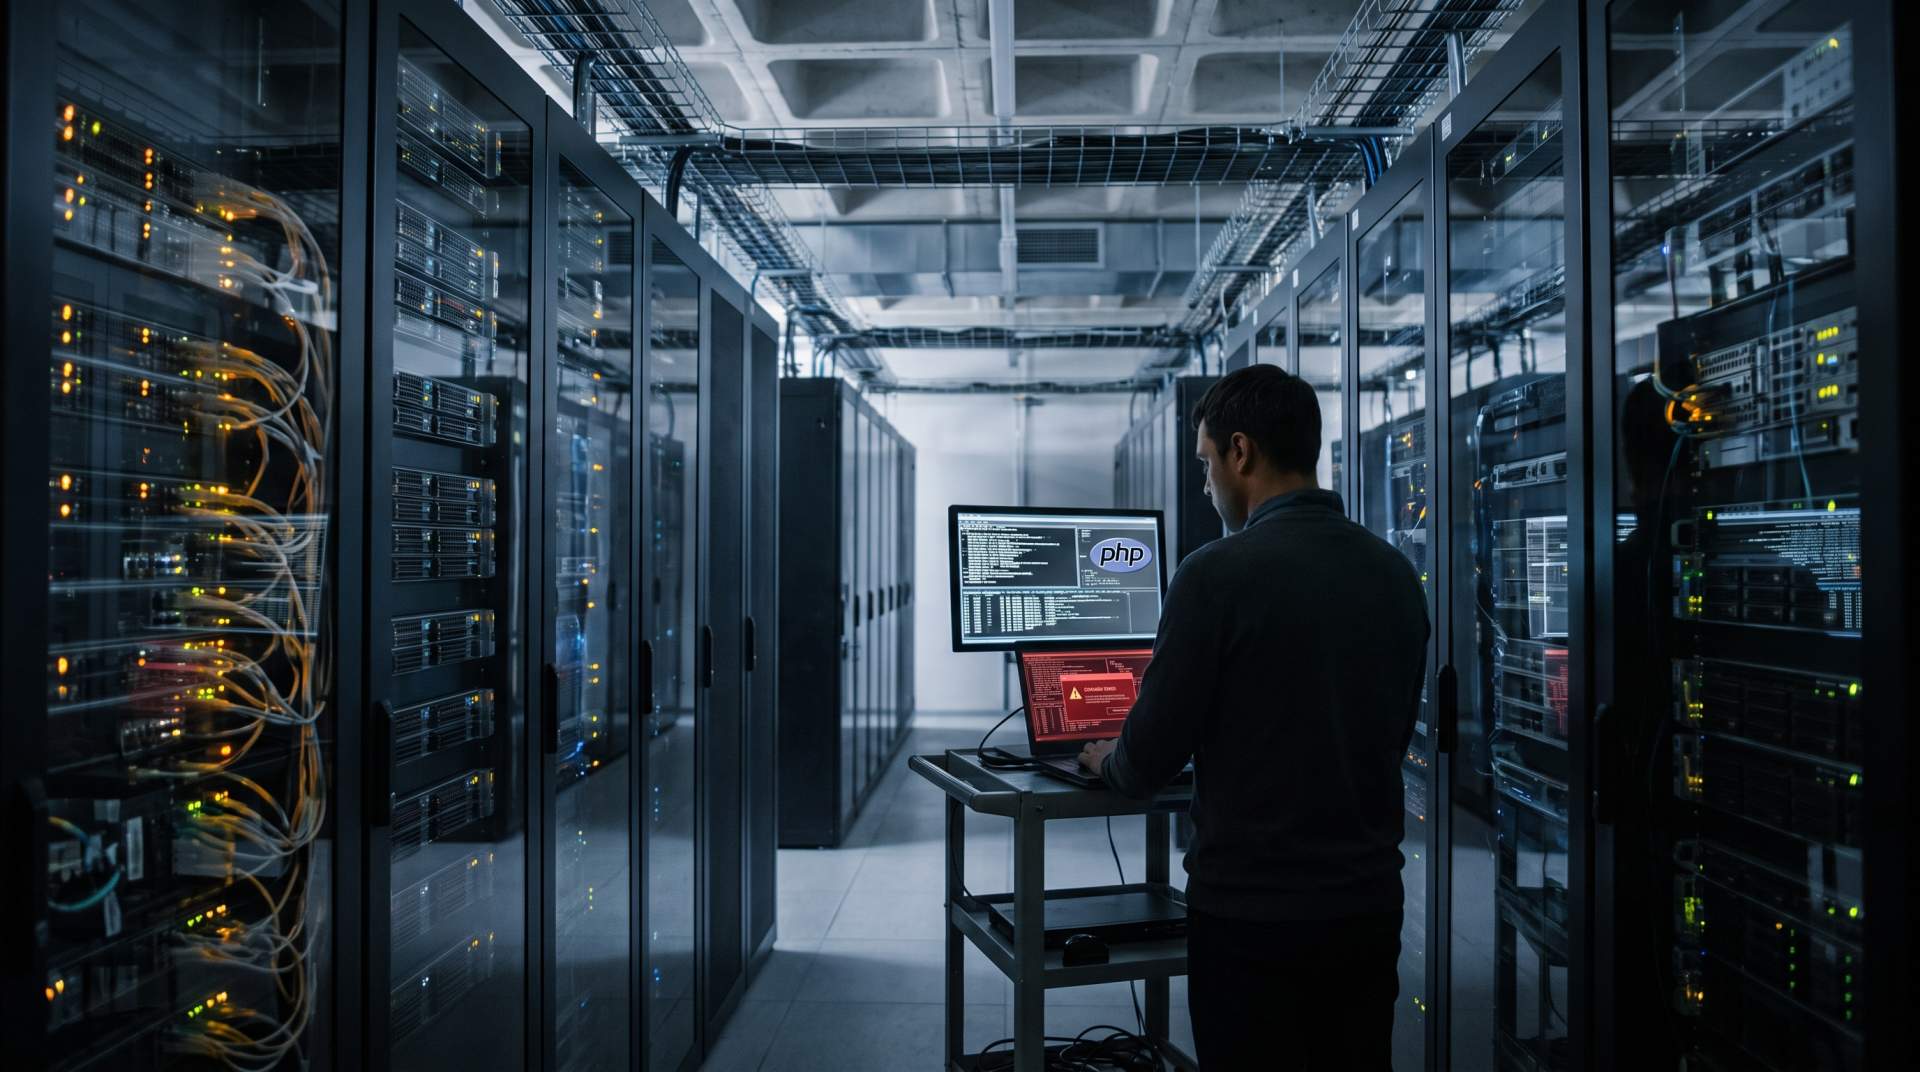
Two critical security vulnerabilities in PHP, a programming language used to power websites and web applications, have triggered an international security response after developers released emergency updates on October 21. Security agencies and technology companies are urging organizations to identify vulnerable systems and install the fixes, while reports of rapidly increasing exploitation attempts highlight the risks of leaving internet-facing servers unpatched.
The vulnerabilities, tracked as CVE-2026-109618 and CVE-2026-109619, could allow attackers to execute malicious code on affected servers without authentication. Both received a critical severity rating of 9.2 under the Common Vulnerability Scoring System, or CVSS. The rating reflects the seriousness of the flaws, although actual exposure depends on the software version, server configuration and other conditions.
The incident is also drawing attention to the expanding role of artificial intelligence in cybersecurity. AI-assisted research contributed to the discovery and investigation of the vulnerabilities, demonstrating how advanced tools can help identify weaknesses in widely used software. The same broader technological shift is also raising concerns about how quickly attackers may turn newly disclosed vulnerabilities into operational threats.
What happened, and why are the flaws serious?
PHP is a server-side programming language. It processes requests, generates dynamic website content and supports many applications that interact with databases. Its widespread use means that vulnerabilities in the language itself can affect organizations across different industries, rather than being confined to a single website or software product.
According to the official PHP security announcement, the two flaws involve problems with internal memory management and request-handling state.
The first vulnerability, CVE-2026-109618, concerns out-of-memory handling. Under certain conditions, PHP may leave internal request data only partially initialized and subsequently treat that data as valid. The second, CVE-2026-109619, involves internal state that can persist after the memory backing it has been freed.
These are low-level software defects, but their potential consequences are significant. If successfully exploited under vulnerable conditions, they could allow an attacker to run code on a server without first logging in.
Depending on the permissions and configuration of the affected system, unauthorized code execution can expose sensitive information, compromise applications or provide a route to further attacks. A vulnerability does not automatically mean that a particular website has been breached, and the existence of a critical flaw should not be confused with confirmation of data theft.
The PHP project released security updates on October 21 and urged users to upgrade immediately.
Emergency updates and rising exploitation attempts
The response has extended beyond software developers. Cybersecurity authorities in Europe and the United Kingdom have advised organizations to identify systems running affected PHP versions, prioritize internet-facing infrastructure and apply available updates.
The European Union Agency for Cybersecurity, the European Commission, CERT-EU, Europol EC3 and national cybersecurity teams issued a joint statement calling for immediate action. Their advice includes coordinating with hosting and service providers to ensure that PHP-based applications receive the appropriate fixes.
The United Kingdom's National Cyber Security Centre has also urged organizations to identify affected systems and monitor exposed services. Where immediate remediation is not possible, organizations should consider taking vulnerable systems offline until they can be secured.
The urgency reflects the possibility that attackers can study publicly available security fixes to understand the weaknesses they address. Once a vulnerability becomes public, organizations that delay updating may face a growing window of exposure.
Reuters reported on October 22 that Cloudflare had observed millions of exploitation attempts following public disclosure of the PHP flaws. That figure describes attempted exploitation activity across Cloudflare's network; it does not establish that millions of servers were successfully compromised.
Organizations have also taken precautionary measures to reduce risk. Reuters reported temporary service suspensions and website outages affecting organizations in several countries as administrators worked to secure vulnerable systems.
These disruptions illustrate a difficult operational trade-off. Keeping an exposed service online without an available fix can create security risks, while taking it offline can interrupt public services, business operations and access to information.
How AI-assisted research contributed to the discovery
The vulnerabilities have also become an important case study in AI-assisted software security.
The PHP Foundation said the security work involved multiple researchers and organizations. Security firm Calif reported finding a critical flaw with the assistance of a large language model, while OpenAI independently reported the same underlying issue. Wiz also independently identified and reported vulnerabilities in the broader investigation.
The findings were examined, coordinated and addressed through work involving researchers, maintainers and other security partners. The PHP Foundation's account also describes how testing environments and additional tools helped researchers validate reports and investigate related attack paths.
This distinction matters. AI did not independently deploy the official patches or replace the people responsible for maintaining PHP. Researchers used AI-assisted methods as part of a broader process that included technical investigation, validation, coordination and software development.
The incident shows how AI can help security teams search for complex defects in established software. At the same time, it highlights the need for careful disclosure procedures, reliable reproduction of findings and enough time for software distributors to prepare fixes before technical details become widely available.
Finding a vulnerability is only one part of the security process. Turning that discovery into a verified patch, distributing the update and ensuring that operators install it are separate challenges.
What website owners and businesses should do
For organizations running PHP-based websites or applications, the immediate priority is to establish whether their systems are affected.
Administrators should identify the PHP versions running across their infrastructure, including systems maintained by hosting companies, third-party vendors or managed service providers. They should then apply the official security updates appropriate to their installations.
The PHP project lists the following patched releases:
PHP 8.5.12
PHP 8.4.27
PHP 8.3.36
PHP 8.2.35
The PHP Foundation says updating is the only safe choice for affected supported installations, and that there are no complete workarounds that replace the fixes. Organizations should follow the official advisory and confirm which update applies to their environment.
PHP 8.2 is approaching the end of its support period, scheduled for December 31, 2026. Organizations using it should plan a transition to a supported version rather than treating the latest patch as a long-term maintenance strategy.
Systems running older PHP releases require particular attention. The PHP project is not providing these fixes for PHP 8.1 and earlier versions that have reached end of life. Administrators using unsupported releases should assess their exposure and plan migration to a supported version. Where immediate remediation is not feasible, restricting or temporarily disabling public access may be necessary.
Updating PHP is not the only step worth taking. Organizations should review server logs for suspicious activity, monitor internet-facing systems, check relevant security advisories from hosting providers and confirm that applications are operating correctly after patches are applied. If there are indications of compromise, security teams should investigate the incident rather than assuming that installing an update resolves any earlier intrusion.
Why the issue matters for Bangladesh
The incident has practical implications for Bangladesh's growing digital economy, even though the available reporting does not establish how many Bangladeshi systems are affected.
Government portals, online businesses, publishers, educational services and other organizations may depend on PHP-based applications. Smaller operators can face particular challenges when they rely on shared hosting or external providers and do not directly manage the underlying server software.
That creates a responsibility for both website owners and service providers. Organizations should ask hosting companies whether their systems have been patched, identify who manages the PHP runtime and establish a clear process for responding to urgent security notices.
For digital publishers, a compromised server can threaten more than website availability. Depending on the attack and the permissions involved, an intrusion could expose administrative accounts, alter published content or affect information stored by an application. These are potential consequences, not confirmed outcomes of the current incident in Bangladesh.
The broader lesson is that cybersecurity depends on maintenance as much as innovation. Investing in new digital services without keeping their underlying software supported can leave avoidable weaknesses in place.
What happens next?
The immediate priority is patching, followed by continued monitoring for exploitation attempts and evidence of compromise. Organizations will also need to review unsupported software, improve coordination with hosting providers and ensure that future security updates can be deployed quickly.
The incident offers a clear example of two sides of the AI-security debate. AI-assisted research can help uncover weaknesses in software that has been used for years, giving maintainers an opportunity to correct problems that might otherwise remain hidden. But disclosure can also compress the time available for organizations to protect themselves.
For PHP users, the most useful response is not to panic or assume that every website has been breached. It is to verify the software in use, apply the appropriate fixes and investigate any credible signs of suspicious activity.

Comments
0